Knowledge / Risk analysis methods
Linked bow-tie models: from one event’s consequence to the next loss of control
Connect a leak, equipment loss and service loss through explicit interface states, preserving one shared barrier identity and consistent probability denominators.
On this page
A release can damage equipment, and damaged equipment can remove a service. Separate bow-ties make those stages readable, but a connector arrow can hide the state information that makes the next stage credible. This original leak-to-service model carries exposure, equipment state and a shared drainage function across the links before attaching any numbers.
Give each linked model one clear top event
Define T1 as loss of primary containment of a specified liquid near two control cabinets, A and B. Define T2 as loss of the specified function of at least one cabinet. Define T3 as delivered service below its required capacity for more than 10 min within a 60 min event mission. Each cabinet can support the full required duty when functioning under the stated conditions.
CAA’s top-event guidance supports manageable linked bow-ties for complex pathways. Here the liquid exposure created after T1 supplies a threat to the cabinet model, while the equipment-loss state after T2 supplies a threat to the service model. Neither connection means that the next top event is inevitable, and the first top event’s frequency is not reapplied at every link.
Write an interface-state contract
A source model should state what it hands to the next model, and the receiving model should identify which of those attributes its response depends on. A common word such as “release” is rarely enough. The same released quantity can produce different cabinet effects if it arrives at a different place, has a different duration or follows a different path.
| Interface | State carried forward | Why retain it? |
|---|---|---|
| I12: leak → cabinets | Liquid/location; arrival and wetting duration; target set; D1 state | A release label alone does not determine equipment effects. |
| I23: cabinets → service | A/B loss vector; remaining capacity; transfer state; elapsed mission time | An equipment-loss label alone does not determine service loss. |
The numerical example below groups those details into a small set of wetting and loss states. It assumes that each group is sufficiently homogeneous for the supplied conditional probabilities. The interface register still records the underlying conditions. If residual timing, conductivity, support state or access changes the next response, refine the groups rather than treating a convenient label as a complete physical description.
Give the shared drainage function one identity
Call the physical drainage function D1. It can appear in the release-spread discussion and in the cabinet-exposure discussion because it influences both descriptions of the same pathway. Use the same identifier, function definition, state and evidence record in both places. Two drawn copies represent one physical function, not two independent drains or two opportunities to earn numerical protection credit.
HSE’s control-systems guidance calls for explicit treatment of shared utilities, environments and dependencies. Here D1 has a stipulated functional probability of 0.8 conditional on the leak; its unavailable probability is 0.2. The function’s state is selected once for the modeled event and passed through the links. A later recovery or state change would need an explicit time-dependent extension.
Condition the exposure states on that one drainage state
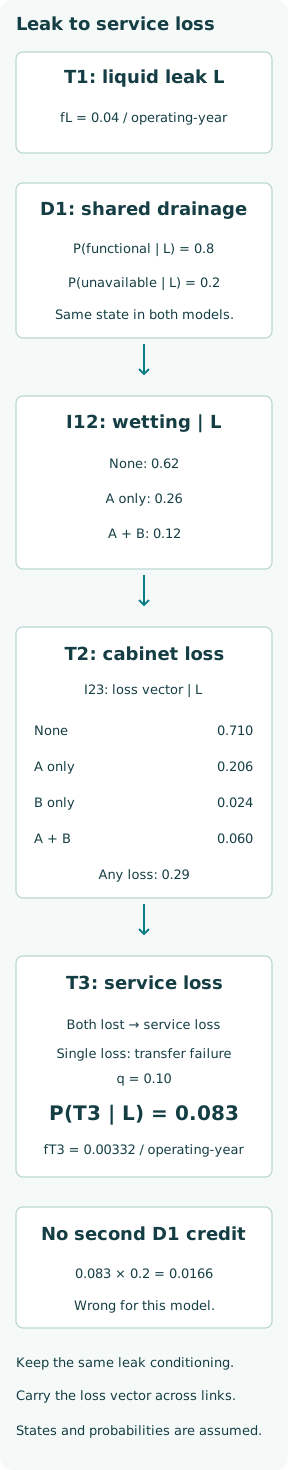
When D1 is functional, stipulate wetting probabilities of 0.75 for no cabinet exposure, 0.25 for A-only exposure and zero for common A+B exposure. When D1 is unavailable, the corresponding probabilities are 0.10, 0.30 and 0.60. Both rows sum to unity. Functional drainage is not assumed to prevent every local splash or every cabinet exposure.
Weighting by D1’s state gives P(no wetting | L) = 0.8 × 0.75 + 0.2 × 0.10 = 0.62. A-only wetting has probability 0.26, and common wetting has probability 0.12. These three probabilities remain conditional on the leak L. They already include the single drainage-state mixture; no extra D1 failure factor belongs after them.
Propagate exposure into the joint equipment state
Assume no wetting causes no cabinet loss. With A-only wetting, A loses its function with probability 0.70 while B remains functional. With common wetting, stipulate joint loss probabilities of 0.10 for neither, 0.20 for A only, 0.20 for B only and 0.50 for both. This joint law is supplied directly and does not assume independent cabinet vulnerabilities.
| A lost | B lost | Probability |
|---|---|---|
| 0 | 0 | 0.710 |
| 1 | 0 | 0.206 |
| 0 | 1 | 0.024 |
| 1 | 1 | 0.060 |
For example, A-only loss is 0.26 × 0.70 + 0.12 × 0.20 = 0.206. The no-loss probability is 0.62 + 0.26 × 0.30 + 0.12 × 0.10 = 0.710. Any equipment loss has probability 0.29, and exactly one cabinet loss has probability 0.23. Preserve the complete loss vector rather than merging all three damaged states into one undifferentiated label.
Resolve service loss from the surviving capacity
If both cabinets lose their functions, the service endpoint occurs. If exactly one is lost, the surviving cabinet has sufficient capacity, but the defined duty-transfer function fails with probability 0.10 conditional on that single-loss state. If neither is lost, the service is maintained in this toy family. These assumptions include the mission and duration criterion; they are not inferred from the diagram.
Consequently P(T3 | L) = 0.060 + (0.206 + 0.024) × 0.10 = 0.083. The single-loss states contribute only when transfer fails, while the both-lost state contributes directly. Calling all equipment loss service loss would instead use 0.29 and ignore surviving capacity. Calling every single loss harmless would omit the transfer requirement.
Attach the initiating frequency once
Let the leak-family frequency be an invented 0.04 per operating year for the same configuration and exposure basis. Multiplying it once by 0.083 gives a service-loss frequency of 0.00332 per operating year. The computation follows a coherent conditional state model from one leak family to one defined final endpoint; it does not multiply three qualitative bow-tie risk ratings.
The event mission limits the consequence calculation; it does not convert the operating-year frequency into a calendar-year probability. Other leak locations, faults unrelated to leakage and later recovery are outside the numerical family. The three linked models can be extended to those cases only with compatible new initiating populations, state transitions and endpoint definitions, avoiding overlap with the existing family.
Do not count D1 again in the receiving diagram
CAA’s recovery-control guidance cautions that drawn controls need not be sequential or independent. If the analyst multiplies the final 0.083 by another D1 unavailability factor of 0.2, the result becomes 0.0166 and the annual frequency 0.000664. That is wrong for this model: the upstream state mixture already includes D1, including local exposure while it is functional.
A useful cross-check calculates service loss separately for each D1 state. The functional-state result is 0.0175; the unavailable-state result is 0.345. Their mixture is 0.8 × 0.0175 + 0.2 × 0.345 = 0.083. This checks the linked calculation without treating either drawing of D1 as an additional probabilistic event.
Keep denominators and known states visible
The equipment table is conditional on L, not on reaching T2. If a receiving model is defined only for events with equipment loss, renormalize its input state masses by 0.29. Its conditional service-loss probability is then 0.083/0.29, approximately 0.286207. Multiplying 0.04 × 0.29 by that conditional value returns 0.00332 per operating year.
Using the unnormalized 0.083 after already multiplying by 0.29 would count the equipment-loss restriction twice. Likewise, if D1 is known unavailable for a particular assessed configuration, the conditional value 0.345 is relevant within this example; the population mixture is not. A design change that alters the mix of exposure states can invalidate an old averaged downstream response even when the connecting label stays the same.
Audit the links as part of the model
Check that each conditional state partition sums to unity, that every outgoing state has a receiving interpretation and that shared barriers retain one physical identity. Trace the event and parameter identifiers through all calculations. Review any feedback loop explicitly: if service loss changes drainage, the one-way model used here may be inadequate and the joint timing must be reconsidered.
The completed argument contains three defined top events, two interface contracts, one D1 identity and a reproducible endpoint calculation. The bow-ties communicate the causal structure; the separate state model supplies the arithmetic. Their connection is defensible only while the physical conditions, conditioning populations and barrier identities remain consistent from the initial leak to the final service loss.